For years, Google has been actively seeking ways to encourage website owners to implement SSL certificates. SSL allows websites to be accessed over HTTPS, which encrypts information sent between the visitor and web server.
Recently, we discussed how Google is moving from a reward system to a punitive one. Websites using SSL continue to get an SEO boost since it became a confirmed ranking signal in 2014, but we noticed a few months ago that Google was blacklisting non-HTTPS websites that allowed password fields and credit card forms to be filled.
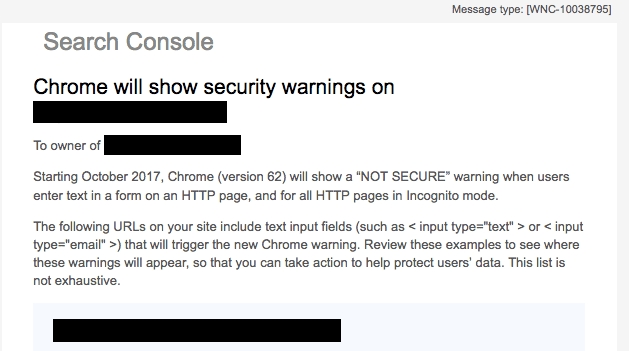
In just 2 weeks, Chrome version 62 will be released, and websites with any kind of text input will require an SSL certificate if they want to avoid a “Not Secure” warning in the address bar.
Make sure your site is verified in Google Search Console to enable email warnings and notices.
It’s unclear at this point if this is a step toward blacklisting sites that take form input without SSL. If so, it makes sense from Google’s perspective. As more sites adopt SSL, the remaining websites will require additional incentive to make the switch. We’ve seen Google ramp this up continuously, and we don’t expect any change in pace.
Users, as we know, often don’t notice the “Not Secure” warnings. The onus is on service providers and website owners to protect their users from unknowingly sending sensitive information to their servers, and Google is taking on the role of policing this.
Is Your Site Affected?
Here are a few questions to ask yourself:
Does your site take any text input? This includes contact forms, search bars, login panels, etc.
Is your website using HTTP:// in the address bar?
If you answered “yes” to both of those questions, you need to implement SSL to avoid showing a “Not Secure” warning in visitor’s browsers. You should also be forcing HTTPS on your site to avoid having users accidentally access the non-encrypted version of your site.
How to Get SSL
Often, your host will have options for enabling SSL. Many hosts even have a one-click SSL option which allows you to auto-generate a free Let’s Encrypt certificate. If you are a Sucuri customer, all plans include free SSL certificates.
Note: There is no difference between paid SSL certificates and free ones when it comes to the level of encryption. If you require more support, you might consider paying for one.
To implement a free Let’s Encrypt certificate on your own server:
Gain administrator access to your web server (sudo over SSH)
Find out what operating system and server software you use.
Get the right instructions for your server at the CertBot website.
Follow the steps to generate your certificate and enable auto-renew.
You may need to contact your host to get the information and access you need.
Get Your Website Converted to SSL Now
[yikes-mailchimp form="7"]
Conclusion
It’s been more than a year since Let’s Encrypt left beta; it’s time for all website owners, hosts, agencies, and service providers to make the jump. There is increasing evidence that the longer you wait, the more risk you have of becoming blacklisted or labeled as “Not Secure”.
In July, at MozCon (a prominent event for SEO), Dr. Pete gave a talk on the top tips for SEO in 2017. At the top of his list was a recommendation to implement SSL. The benefits and risks are becoming hard to ignore.
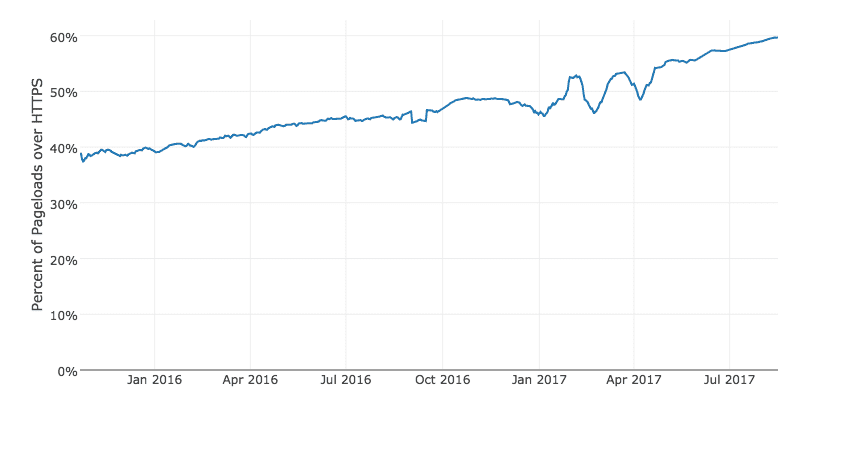
According to Firefox telemetry, almost 60% of web pages today are loaded via HTTPS. We expect this number to increase as Google finds more ways to penalize sites that should be using the encrypted protocol to protect sensitive input.
From our perspective, this increased focus on SSL is a good thing for website owners. Hopefully, this leads to more interest in website security in general, because unfortunately, even with SSL, websites are still at risk of being hacked and controlled by attackers.
The distinction here is that SSL does not mean the website is secure. While HTTPS keeps the visitor’s information secure in transit, SSL doesn’t do anything to protect the website from being hacked.
Original Article
Cookie Consent
We use cookies to improve your experience on our site. By using our site, you consent to cookies.
ID used to identify users for 24 hours after last activity
24 hours
_gat
Used to monitor number of Google Analytics server requests when using Google Tag Manager
1 minute
__utmt
Used to monitor number of Google Analytics server requests
10 minutes
__utmb
Used to distinguish new sessions and visits. This cookie is set when the GA.js javascript library is loaded and there is no existing __utmb cookie. The cookie is updated every time data is sent to the Google Analytics server.
30 minutes after last activity
__utmc
Used only with old Urchin versions of Google Analytics and not with GA.js. Was used to distinguish between new sessions and visits at the end of a session.
End of session (browser)
__utmz
Contains information about the traffic source or campaign that directed user to the website. The cookie is set when the GA.js javascript is loaded and updated when data is sent to the Google Anaytics server
6 months after last activity
__utmv
Contains custom information set by the web developer via the _setCustomVar method in Google Analytics. This cookie is updated every time new data is sent to the Google Analytics server.
2 years after last activity
__utmx
Used to determine whether a user is included in an A / B or Multivariate test.
18 months
_ga
ID used to identify users
2 years
_gali
Used by Google Analytics to determine which links on a page are being clicked
30 seconds
_ga_
ID used to identify users
2 years
_gac_
Contains information related to marketing campaigns of the user. These are shared with Google AdWords / Google Ads when the Google Ads and Google Analytics accounts are linked together.
90 days
__utma
ID used to identify users and sessions
2 years after last activity
Google reCAPTCHA helps protect websites from spam and abuse by verifying user interactions through challenges.
Name
Description
Duration
_GRECAPTCHA
Google reCAPTCHA sets a necessary cookie (_GRECAPTCHA) when executed for the purpose of providing its risk analysis.
179 days
You can find more information in our Cookie Policy and .